


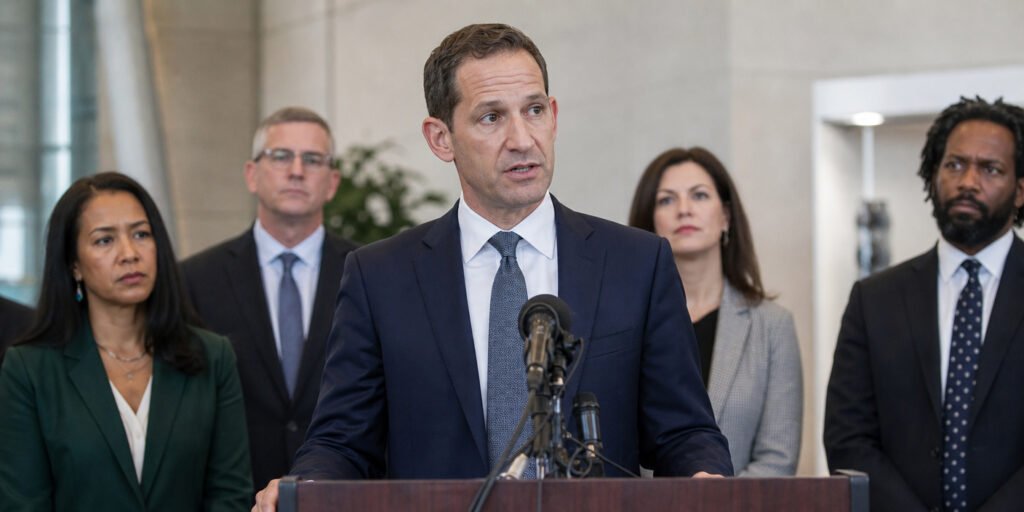
San Francisco Mayor Daniel Lurie has formally introduced a robust new privacy policy governing the city’s public safety camera network. This initiative marks a significant policy pivot, designed to harmonize the city’s ongoing efforts to drive down crime rates with the essential protections of civil liberties for residents, business owners, and visitors alike. The comprehensive framework addresses long-standing concerns regarding surveillance, data stewardship, and the role of third-party vendors, signaling a new era of accountability in municipal technology infrastructure.
Key Highlights
- Strict Retention Limits: New, mandated timelines for how long data can be stored, preventing indefinite surveillance logs.
- Local Control: A requirement that all footage remains under the direct jurisdiction of local municipal entities, preventing third-party or cloud-based data silos.
- Vendor Accountability: Implementation of rigorous cybersecurity and privacy audits for all city contractors, ensuring data is not mishandled by external technology partners.
- Transparency Framework: Clearer guidelines for when and how footage can be accessed, limiting scope creep in investigative procedures.
Establishing the New Digital Standard for Urban Safety
The integration of technology into public safety—ranging from license plate readers to high-definition security cameras—has become a hallmark of modern city management. However, in San Francisco, the proliferation of these devices has historically been met with intense scrutiny from civil rights groups and privacy advocates. Mayor Daniel Lurie’s recent policy announcement represents a calculated attempt to reconcile the imperative of public order with the city’s legacy of prioritizing personal freedom.
The Three Pillars of Data Governance
At the core of the new policy are three distinct pillars that dictate how the city interacts with the massive amounts of data generated by its safety infrastructure.
First, the Retention Schedule is the most immediate change. Previously, the lack of a unified municipal standard often led to fragmented data storage. Under the new protocol, retention periods are strictly capped, ensuring that data is purged according to a predictable, policy-driven schedule. This minimizes the risk of long-term profiling and reduces the city’s liability regarding data breaches.
Second, the principle of Local Control serves as a firewall against external influence. The policy mandates that the city’s security infrastructure must not rely on proprietary, opaque cloud storage solutions managed by third-party vendors. Instead, footage must remain within the secure, local purview of municipal departments, specifically the San Francisco Police Department (SFPD) and IT oversight committees. This ensures that the city, not a corporation, decides the lifecycle and accessibility of public surveillance data.
Finally, the Vendor Accountability measures address the supply chain of surveillance technology. Historically, security software provided by private tech firms often operated as a “black box.” The new directive requires that any vendor providing cameras, software, or data management services to the city must undergo rigorous, recurring security and privacy audits. These audits ensure that the technology complies with SF’s local privacy ordinances—a move that effectively holds contractors to the same standard as city employees.
Balancing Safety with Civil Liberties
Mayor Lurie’s announcement comes at a time when San Francisco is under intense pressure to address retail theft, organized crime, and property safety. Critics of surveillance often argue that such tools, once installed, tend to expand in scope without democratic oversight. By codifying these protections now, the administration is proactively answering those concerns. The objective is to ensure that while the technology is effective at deterring crime, it cannot be weaponized or misused for unauthorized tracking or data mining.
This “safety-first, privacy-always” approach is designed to rebuild public trust. The administration contends that by making the rules of surveillance clear, predictable, and transparent, the city can actually deploy these tools more effectively. When the public understands the limitations of the data collection, they are less likely to perceive the cameras as an invasive “Big Brother” presence, and more as a surgical tool for municipal safety.
The Economic and Technical Implications
Beyond the policy ramifications, there is an economic component to this initiative. By forcing vendors to meet strict, bespoke privacy standards, San Francisco is setting a regional benchmark. Tech companies wanting to bid on SF government contracts must now invest in “privacy-by-design” features. This may initially increase costs for the city, but it serves to insulate the municipality from the massive potential costs of data breaches, civil rights lawsuits, and the reputational damage associated with unauthorized surveillance.
This policy shift also aligns with broader trends in cybersecurity. In an era where data is often described as the “new oil,” municipal governments are increasingly becoming targets for sophisticated cyber-attacks. By mandating local control and rigorous vendor oversight, the city is effectively hardening its digital perimeter. This makes the infrastructure not just more “private” in a legal sense, but more resilient in a technical sense.
A Blueprint for Modern Cities
Looking toward the future, the success of this policy will be measured by its implementation. The challenge lies in enforcement: will the administration be able to maintain these standards as technology evolves? AI-integrated analytics and facial recognition are on the horizon. The current policy, by establishing clear ownership of data and strict vendor criteria, provides a foundation that can be expanded to include these emerging technologies. It is not a static set of rules, but an evolving framework intended to ensure that San Francisco leads by example in the management of urban intelligence.
As the city continues to navigate the complexities of 21st-century urban life, Mayor Lurie’s focus on privacy policy suggests a strategy where governance must catch up with innovation. By institutionalizing these protections, the administration aims to prove that public safety and individual privacy are not mutually exclusive—provided the city has the will to enforce the guardrails.
FAQ: People Also Ask
Q: How long will data be retained under the new policy?
A: The specific retention window is determined by the updated municipal schedule, which moves away from indefinite storage toward strict, activity-based purging timelines to ensure minimal data exposure.
Q: Does this policy affect private cameras owned by local businesses?
A: No, the current policy strictly applies to the city’s public safety camera network, which is owned and operated by the municipality. It does not regulate private businesses, though it sets a standard for how those businesses might voluntarily align with city privacy goals.
Q: Who is responsible for enforcing the vendor audit requirements?
A: Compliance is managed by the city’s IT and procurement departments in collaboration with oversight committees, ensuring that third-party contractors meet cybersecurity and privacy mandates before any contract renewal or new deployment.
Q: Why was this change necessary now?
A: The policy was introduced to address public concerns regarding the scope of surveillance, reduce city liability, and create a transparent framework that allows for effective crime reduction without infringing upon the civil liberties of residents.
More Stories
Global Election Tensions: Legal Battles in CA, High Stakes in Brazil
US Envoy Witkoff Labels Putin ‘Humanitarian’ in Peace Push
Toledo Hazmat Crisis: Mass Evacuations Ordered for North Side